“The gap between what management reports and what's actually happening is widest when no one on the board knows which questions to ask.”
Three tools
Three Tools.
Use them together — each one makes the other ones more useful.
01
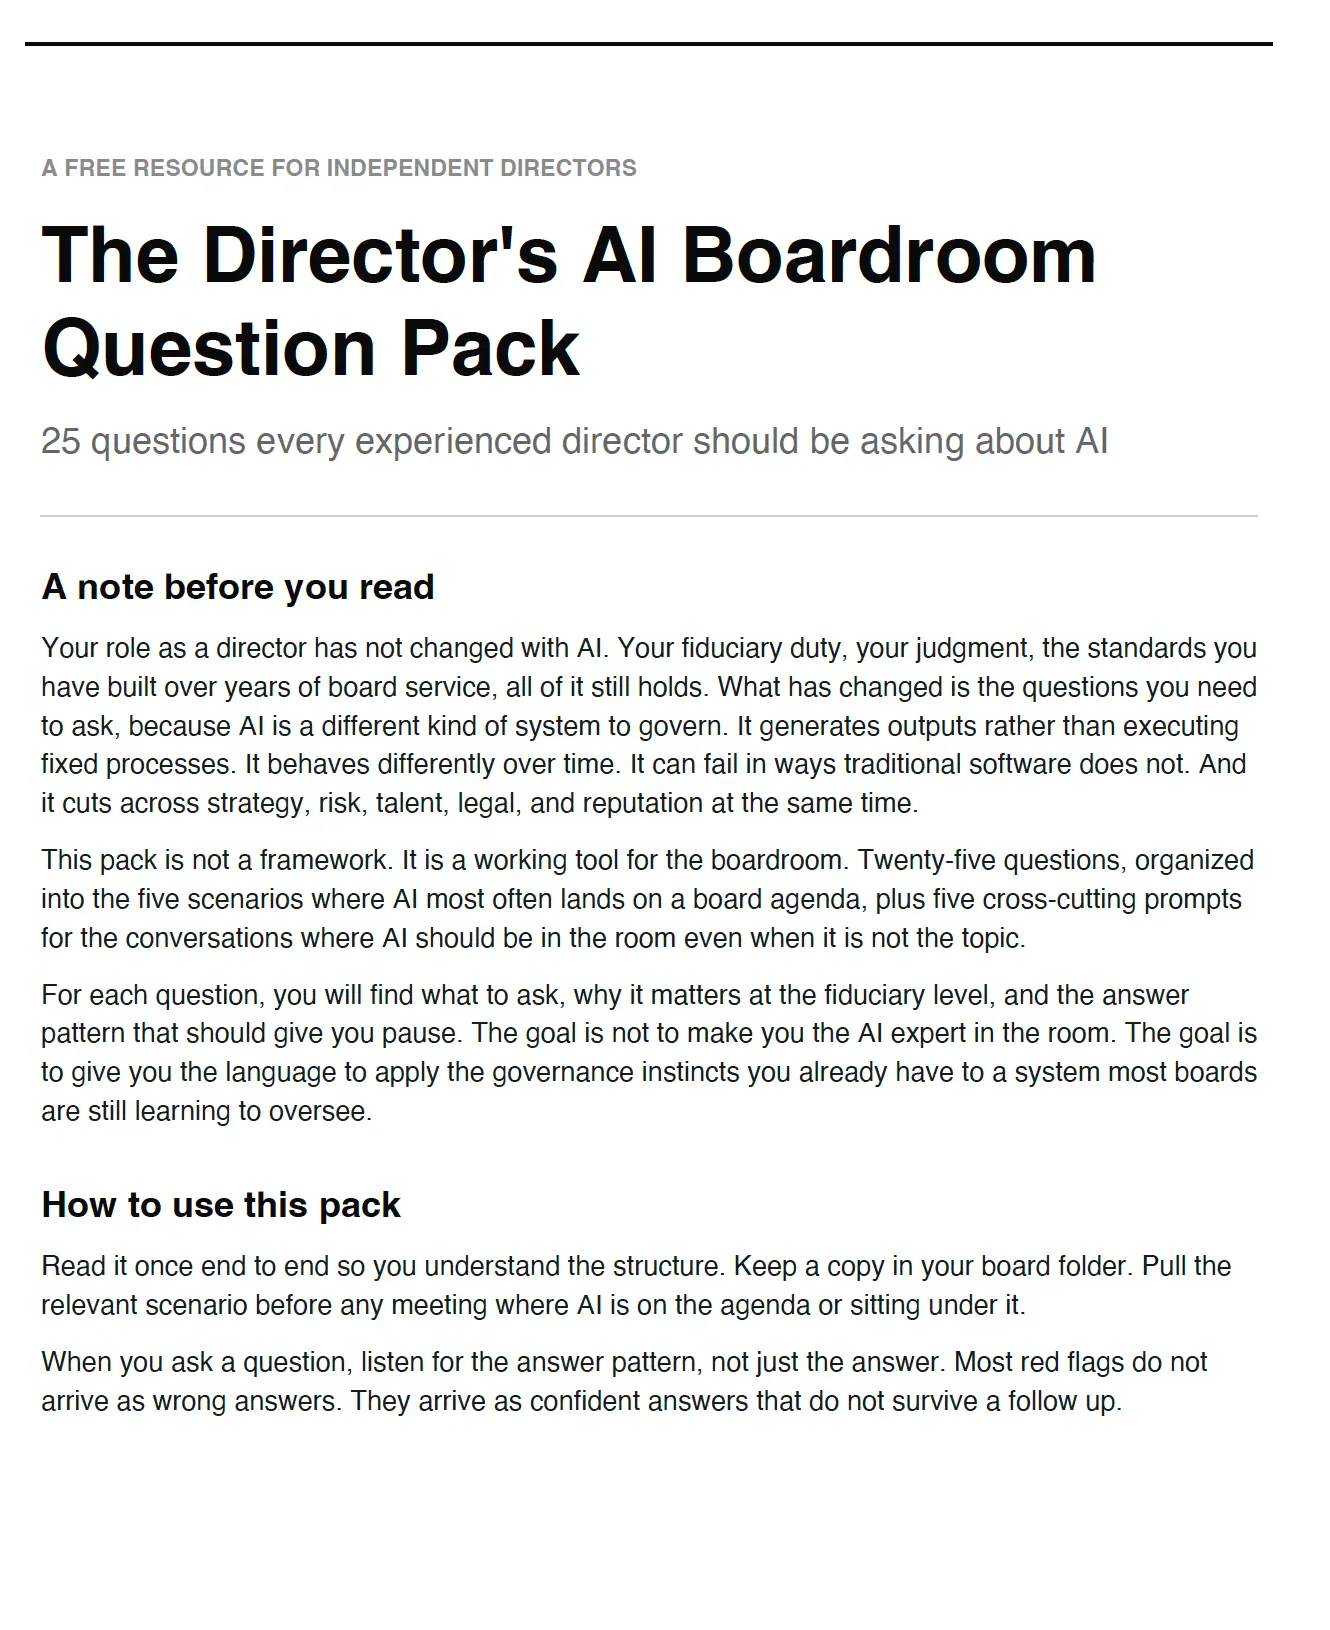
25 Questions Every Director Should Ask About AI
AI is a different kind of system to govern. Your fiduciary duty hasn't changed, but the questions you need to ask have. This working tool provides the language you need to apply your governance instincts to a system most boards are still learning to oversee. Move past the hype and start the conversations that matter.
“What are the kill criteria for this AI system, and who has the authority to invoke them?” — a sample from inside the pack.
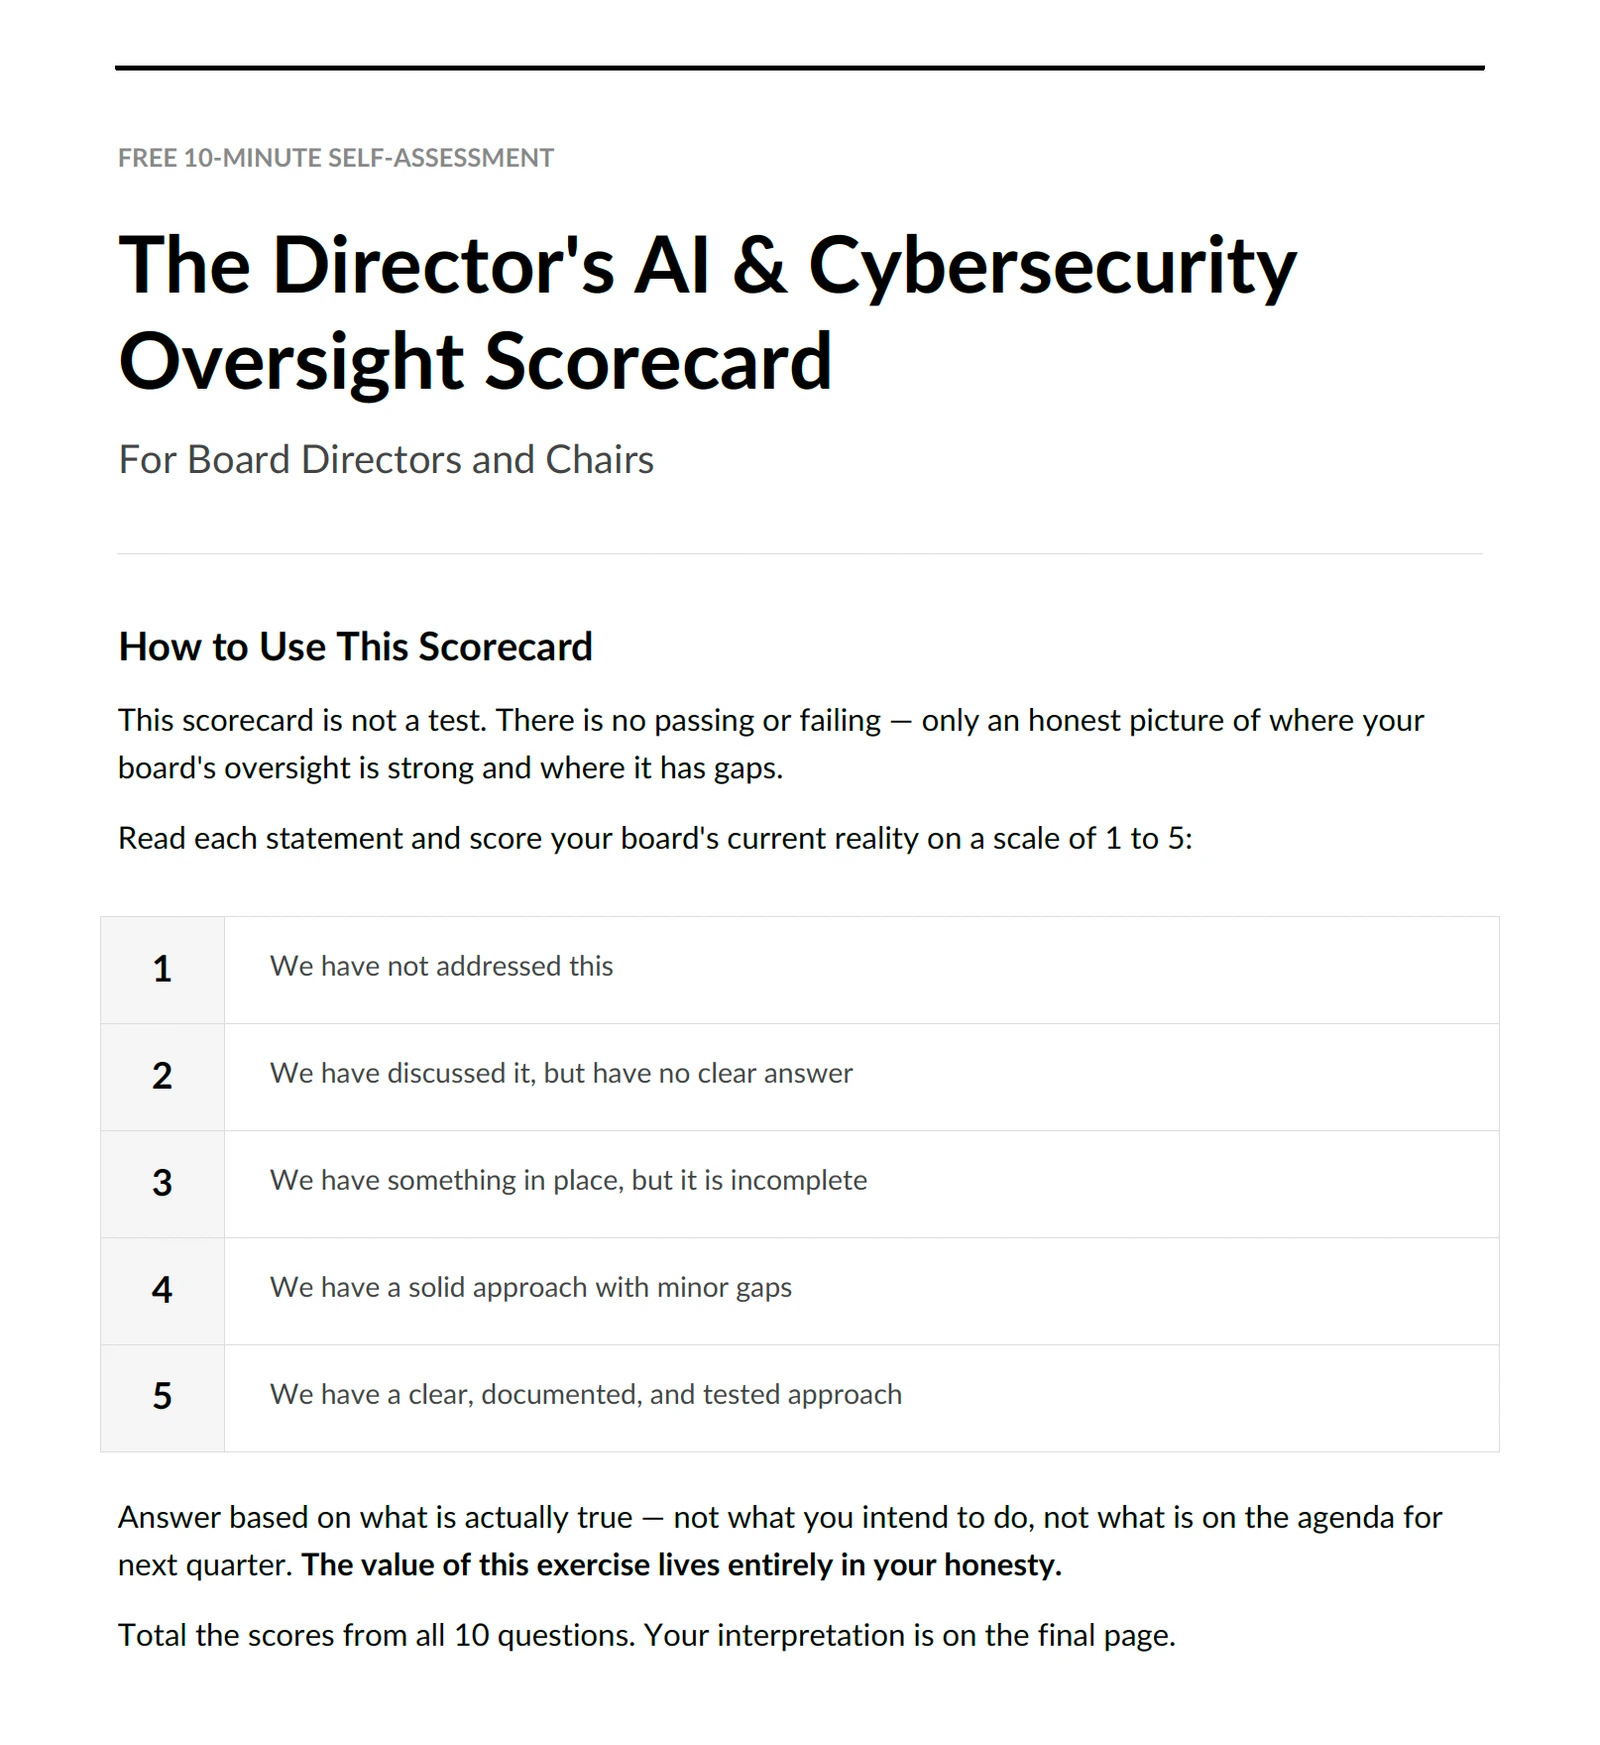
Most Boards don't know they have a clarity gap until a crisis occurs. Our 10-minute scorecard helps you to identify your blind spots and provides a baseline for better decision-making.
10 minutes. Five dimensions. An honest picture — not a sales pitch.
Reports & Learnings for the Boardroom is where Tyson Martin translates AI, cybersecurity, digital risk, and technology governance into plain-English insight for directors, CEOs, and executive teams.
These are not technical deep dives for specialists. They are practical briefings for leaders who need to ask better questions, see risk earlier, understand opportunity faster, and make decisions they can defend.
The questions you ask in the boardroom are only as sharp as the information behind them.
Plain-English AI, cybersecurity, & technology governance insights — biweekly, written for directors, not technologists. 329 articles. No jargon. No pitch.
I.
Cut through the jargon
Technical trends translated into the language your fiduciary duty requires.
II.
Defensible decisions
Decision rights and reporting structures that protect the board from digital liability.
III.
Strategic oversight
From reactive compliance to proactive resilience — without stalling innovation.
Cybersecurity integration after acquisition: use this 90-day executive plan to clarify ownership, reduce risk, test recovery, and protect enterprise value.
Cyber due diligence tells a buyer what they are actually acquiring before a deal closes. Here is what it covers, the red flags that reprice a deal, and why it now sits on the board's desk.
Agentic AI vendor risk can hide who controls your data and systems. Learn how to limit authority, assign owners, test recovery, and defend board decisions.
Use an agentic AI risk register to set ownership, autonomy limits, approval thresholds, and evidence before deployment creates business exposure.
· 10 min read
Book a Decision-Clarity Call
You've seen what these tools reveal. Let's close the gaps they found.
Directors who have used the Question Pack in a board meeting, scored their board's readiness, and read the reports have a very clear picture of where their oversight stands. The next step is a 30-minute conversation about what to do about it.
A direct discussion about your mandate and the pressure driving it
An honest read on fit, including whether Tyson is the wrong answer
Something you can take back to your board or search committee