The Seasonal Staff Problem: Security for the Workforce That Leaves in October
Maine's seasonal economy doubles the workforce every summer and halves it every fall. Access that arrives fast and leaves slowly is the quiet risk of the season.

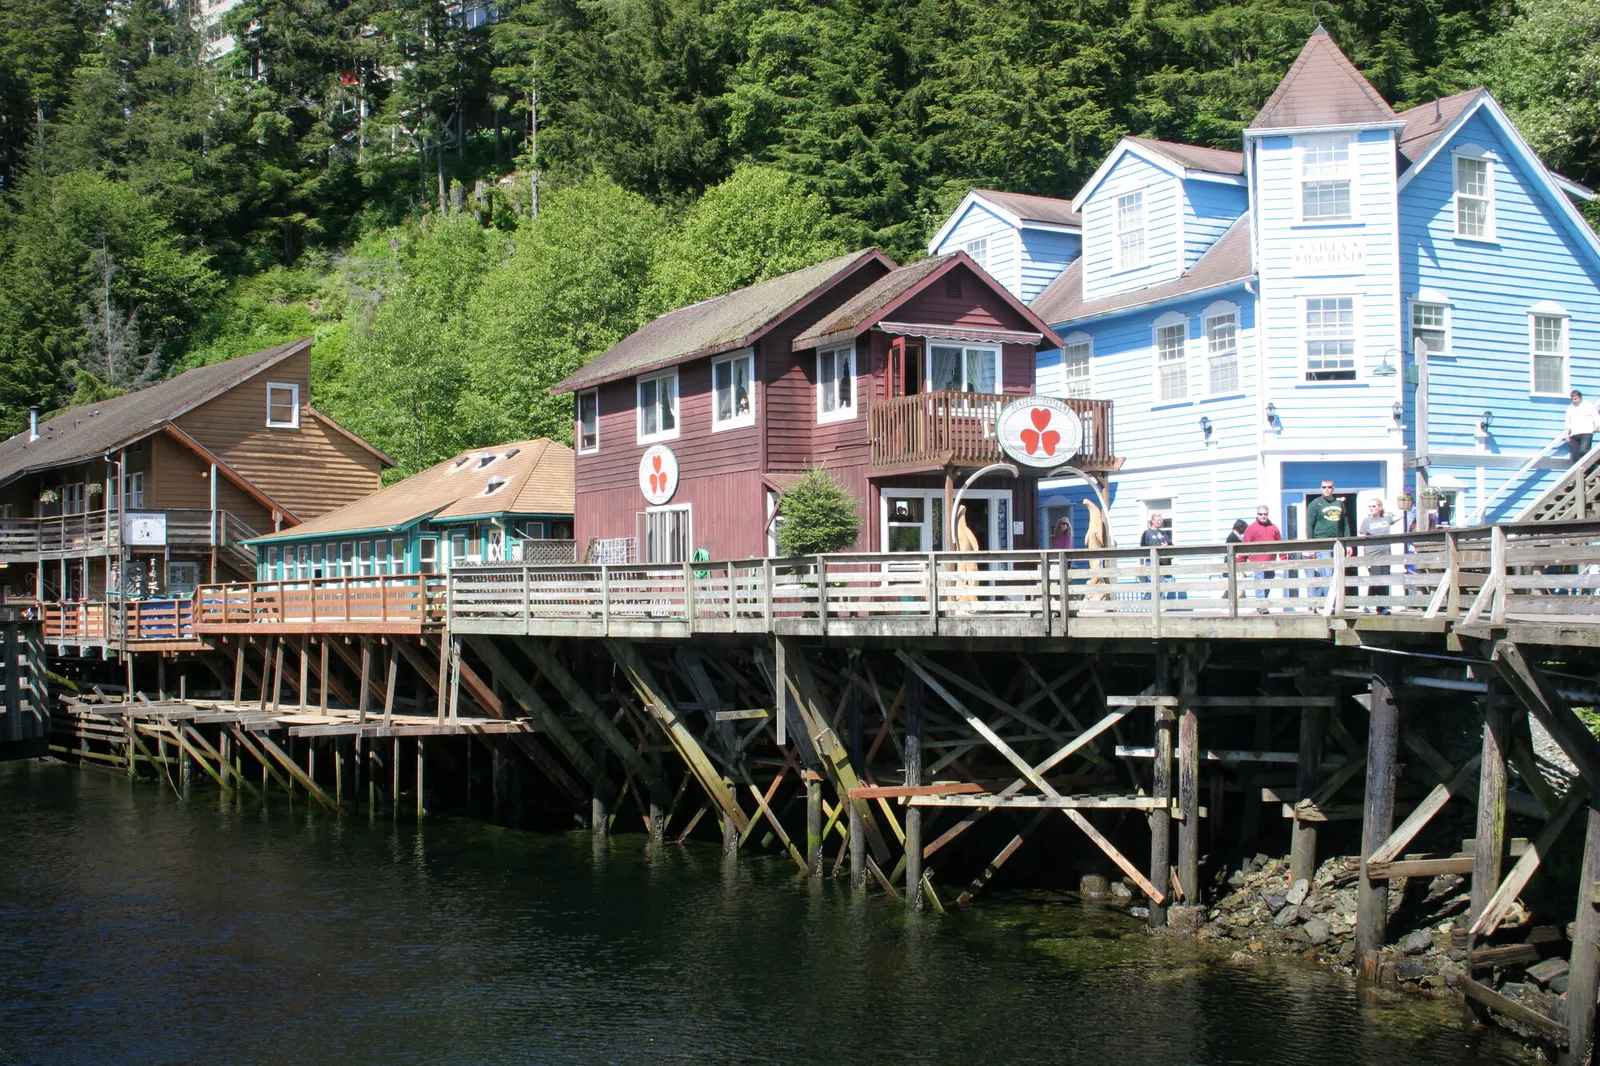
In June, the inn's headcount goes from fifteen to forty. By the end of October it is fifteen again. The twenty-five seasonal hires needed the booking system, the card terminal, and the shared email on their first morning, and most of them got it with the same shared login as last summer's crew.
Seasonal businesses run on this rhythm, and their security exposure runs on it too. Access granted in a hurry in May tends to leave on its own schedule in November, or not at all. The former housekeeper's phone still gets the booking notifications; last year's dockhand still has the supplier portal password in an old text thread.
None of this requires a security program to fix. It requires three habits timed to the season: fast in, clean out, and a fall sweep before the doors close.
TLDR
Seasonal access should be role-based and pre-built, so day-one setup takes minutes.
Every seasonal account gets an end date at creation, not a reminder in October.
Shared logins are the default failure mode; replace or wrap them before the season starts.
The fall sweep closes what the process missed: accounts, devices, door codes.
Next year's setup is this year's documentation, written while the season is fresh.
Fast in: the day-one package
The seasonal rush does not tolerate a week of account setup, and it does not have to. Build the day-one package before the season: for each seasonal role, the standard accounts, the systems, and the training that fits in the first morning.
The package approach does double duty. It makes onboarding fast when the lobby is full, and it makes access uniform, so the fall cleanup knows exactly what each role had. The same onboarding logic applies year-round; the discussion of what Maine nonprofit boards should ask about cyber covers the governance side for the state's many seasonal-adjacent organizations.
Clean out: end dates at creation
The single most effective habit costs nothing: every seasonal account is created with its end date set. The booking system account expires November 1. The email forward stops. The door code changes.
This fictional example shows a coastal inn's seasonal access table. It is an illustration, not a prescription.
| Role | Systems | End date set | Fall check |
|---|---|---|---|
| Front desk seasonal | Booking, email, card terminal | Nov 1 | Accounts disabled, terminal users removed |
| Housekeeping | Scheduling app, door codes | Nov 1 | App access removed, codes rotated |
| Kitchen seasonal | Ordering, scheduling | Nov 1 | Accounts disabled |
| Dock and launch | Fuel system, supplier portal | Nov 1 | Portal password changed |
Where the system does not support expiry, the calendar does: a recurring reminder in late October with the list of what to close.
The shared login question
Seasonal operations love shared logins because they are fast, and the reasons are real: per-seat pricing, one terminal at the dock, a crew that turns over twice a season. The answer is rarely a ban; it is picking the right fix per case from the earlier discussion of breaking the shared-login habit.
For the card terminal and the booking system, per-user access is worth the small cost because money and customer data are involved. For the crew scheduling board, a wrapped shared login from the password manager, changed each fall, may be the honest proportionate answer.
The October sweep and the June advantage
The fall sweep is one afternoon: disable the accounts on the list, collect the keys and codes, confirm the forwarding stopped, rotate what was shared. Then, while the season is fresh, write down what the business learned: which roles needed what, what the day-one package missed.
That note is next June's advantage. The seasonal business that documents this year's access is the one whose next season starts with a checklist instead of a scramble, and whose risk leaves with the crew.
The related discussion of maine nonprofit boards is worth your time alongside this one. The related discussion of interim ciso in maine is worth your time alongside this one.
Frequently asked questions
We are a ten-person operation. Is this overkill?
The habits scale down: one role list, end dates on accounts, one fall afternoon. Small seasonal businesses are exactly where the shared login from 2019 still works, so the payoff is proportionally larger.
What about returning seasonal staff?
Rehire them with the same day-one package and fresh credentials. Returning does not mean the old access lived on; it means setup is fast because the role is already defined.
Does cyber insurance care about this?
Increasingly yes. Applications ask about access management and offboarding, and the honest answer for a seasonal business is either a process like this one or a finding waiting to happen.
A Defensible Next Step
Before this season ends, set the date for the October sweep and write the access list it will work from. Twenty minutes of preparation now is the difference between a workforce that leaves in October and access that does not. Book a Decision-Clarity Call if you want the seasonal package built for your operation.
Get Board-Ready on AI and Cyber Risk
A 30-minute call. No charge. You'll leave with a clear read on where your oversight stands and what to do about it.
Written by Tyson Martin, NACD.DC
Chief Trust, Security & AI Officer. CISO of record at MIO Partners; former CISO & CTO at Lumber Liquidators and Orvis; advisor to 200+ Fortune 500 boards and C-suites at AWS.
See the track record